New Virtual Machine Server Setup Checklist
Software engineer and founder with a background in finance and tech. Currently building aVenture.vc, a platform for researching private companies. Based in San Francisco.
I use a lot of checklists -- here is one of mine for setting up a new Linux virtual machine server. The commands are written for Ubuntu/Debian-based systems.
System Updates
Update Package Lists and Upgrade System
First, let's update the package lists and upgrade existing packages:
apt update: Updates the package list/index files from repositoriesapt upgrade: Actually upgrades the installed packages to their latest versions
Docker Installation
The Docker commands below are for Ubuntu only. For Debian, follow the separate official Debian installation guide instead.
1. Remove Conflicting Packages
2. Set up Docker Repository
3. Install Docker Engine
4. Configure Docker to Start on Boot
Change Hostname
To permanently change your server's hostname:
And update /etc/hosts to reflect the new hostname:
User Management
Create New User with Sudo Privileges
Essential CLI Tools Installation
Install Homebrew
Login as your new user above first, as you can't install homebrew as root.
Follow the installer's printed Next steps to add brew to your shell before continuing.
Install Micro Editor
Install Lazydocker and Lazygit
SSH Server Configuration
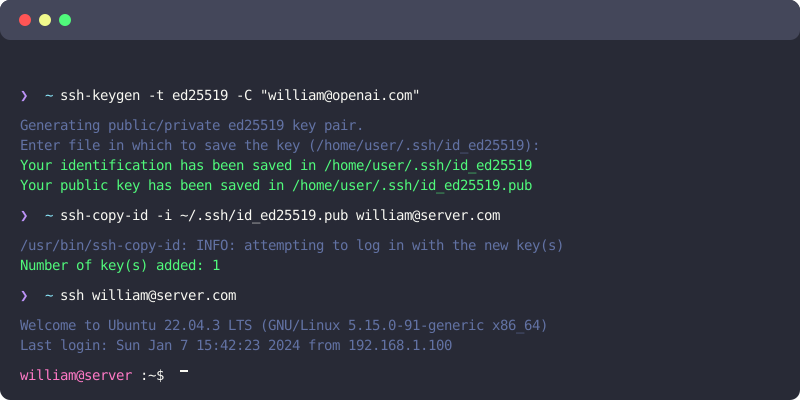
1. Generate SSH Key Pair (on your local machine)
2. Add SSH Keys
For the new user:
3. Test Key Login, Then Configure SSH Server
Keep the current session open. From a new terminal on your local machine, confirm that the new user can log in using a key, without falling back to a password:
In that new session, confirm sudo -v succeeds. Only then disable root/password login by editing /etc/ssh/sshd_config:
Add/modify these important settings:
OpenSSH generally uses the first value it reads: settings included earlier from /etc/ssh/sshd_config.d/*.conf may take precedence over the main file. Check the effective settings with sudo sshd -T and adjust the earlier setting if needed.
4. Restart SSH Service
Validate first, and restart only if validation succeeds:
Repeat the key-only login check in another terminal before closing the existing sessions.
Security Recommendations
- Always keep your system updated
- Don't allow SSH logins via password
- Consider using UFW (Uncomplicated Firewall) to manage incoming connections; allow your SSH port before enabling it (
sudo ufw allow OpenSSHfor the default port, thensudo ufw enable) - Docker-published ports bypass normal UFW rules, so UFW alone does not control access to them
Remember to test SSH access with your new user before closing your current session to ensure you haven't locked yourself out of the server.